Data Protection Lawyer in India · DPDP Act, Data Protection Board, Breach Response, Cross-Border Data

Data Protection Lawyer in India

The DPDP Act allows penalties of up to Rs 250 crore for a single security failure, and the Board that enforces it is already in place. When your company needs an advocate to read the law against your actual systems, contracts and vendors, and to stand with you if the Board comes calling, this is the team. Led by Prakhar Rai, Advocate.

Tell us what data you handle and where you are stuck.

Preparing for DPDP, answering an investor’s privacy questionnaire, dealing with a breach, or reviewing a vendor that touches personal data? Tell us the situation and a data protection advocate will call you back with a clear read on what needs doing, in what order. No obligation. Please do not send personal data of your customers in this form.

Or reach us directly
WhatsApp +91 8004800100 · contact@mylegalpal.com


    Bar Council Advocates · Right of audience
    DPDP-Focused · Indian law first
    Led by Prakhar Rai · Advocate
    Fully Online · Across India

    When you need a data protection lawyer in India, and when a tool is enough.

    Plenty of DPDP work does not need a lawyer on day one. A scan of your website, a checklist, a standard privacy policy: those can get a small business moving. The point at which a data protection lawyer in India earns the fee is when the question stops being “what does the Act say” and becomes “what does it mean for how we actually run”.

    That is a question about your contracts with vendors, the way your product asks for consent, who inside your company has access to what, what happens if something leaks, and whether an investor or an enterprise customer will accept your answers. It is also the point where, if the Data Protection Board of India writes to you, you need an advocate who can reply and appear.

    If you only want a quick self-check, start with our free DPDP compliance checker or the DPDP website scanner. If you want to understand the Act first, our DPDP Act compliance guide explains it in full. This page is about the legal work around them.

    Where DPDP stands currently

    The DPDP Rules were notified in November 2025 and are being phased in. The Data Protection Board of India is already constituted and complaints can be made to it. Consent Manager registration opens around November 2026, and the substantive duties, including notice, consent, security safeguards, breach notification and Data Principal rights, are due by 13 May 2027. There has been official talk of shortening that window, so plan for the earlier date and treat May 2027 as the latest.

    Penalties are set per contravention and can stack. Failing to keep reasonable security safeguards can draw a penalty of up to Rs 250 crore, which is why most boards ask for a legal view well before the deadline. The full timeline and penalty table are in our DPDP Act guide.

    What our data protection lawyers do

    Ten pieces of legal work around DPDP and Indian data law, and the pages that go deeper on each.

    DPDP gap assessment and roadmap

    We map what personal data you hold, why, where it goes and who can reach it, then compare that to what the Act and Rules require. You get a risk-ranked list of what to fix first. For a self-serve first pass, use the DPDP compliance checker.

    Consent and notice design

    Whether your sign-up flow, notices and withdrawal options meet the standard, reviewed against the actual screens and not only the policy text. See the consent management rules and, for the documents, our privacy policy drafting service.

    Vendor and processor contracts

    Anyone who processes personal data for you needs to be bound by a contract that puts your obligations on them and allocates liability. We review and negotiate these, starting from our data processing agreement template where it fits. The wider agreements sit with our contract lawyers in India.

    Significant Data Fiduciary advice

    If the government designates you, you take on a Data Protection Officer based in India, independent audits and impact assessments. We advise on whether you are likely to be caught and how to prepare, including the DPIA.

    Breach readiness and response

    A response plan before you need one, and legal support in the first hours after an incident, when several reporting clocks start together. Our data breach response playbook sets out the structure.

    Cross-border transfers and global groups

    Moving personal data in and out of India, and reconciling DPDP with GDPR and other laws for one product. See data protection laws around the world and our EU work on legal services in the EU.

    Children’s data

    Verifiable parental consent, the ban on tracking and targeted advertising aimed at children, and how that changes product design. Our EdTech lawyer in India page covers it in depth.

    Employee and HR data

    Employment has its own legitimate-use ground under the Act, with limits. We review HR systems, monitoring and background checks. See our employment agreement guide.

    Data Principal requests and grievances

    Setting up how access, correction and erasure requests are received, verified and answered, and how grievances are handled and recorded.

    Data Protection Board proceedings

    Responding to a notice, a complaint or an inquiry, preparing a voluntary undertaking, and appearing for you. Explained in the next section.

    If the Data Protection Board writes to you

    The Data Protection Board of India receives complaints from Data Principals, inquires into breaches and non-compliance, and imposes penalties after giving the party a chance to be heard. That makes it a formal proceeding, with deadlines, written replies and evidence. It is not an inbox.

    What an advocate does at this stage

    We read the notice and the complaint, identify which obligations are actually in question, collect the records that show what you did and when, and write a reply that answers the allegation and no more. We appear on your behalf where a hearing is held. A company that answers a Board notice itself often volunteers facts that make the position worse.

    Voluntary undertaking

    The Act allows the Board to accept a voluntary undertaking from a company at any stage, which can bring proceedings to a close. Whether to offer one, and on what terms, is a legal judgment that depends on how strong the case against you is and what you can commit to.

    Appeals

    An order of the Board can be appealed to the Telecom Disputes Settlement and Appellate Tribunal. The appeal has its own limits and deadlines, so advice on whether to appeal needs to start as soon as an order is received.

    A pattern we see: a company that treated a complaint as customer service, answered informally, and only later realised that the exchange was the record the Board would read. A short call with an advocate the day the complaint arrives costs far less than repairing that record later.

    DPDP is not the only Indian rule on your data

    A company can satisfy the DPDP Act and still be in breach of another Indian rule. Part of a lawyer’s job is to put the rules side by side and apply the stricter one. Section 16 of the Act itself says that where another law gives stronger protection, that law continues to apply.

    Incident reporting to CERT-In

    CERT-In’s 2022 directions require certain cyber incidents to be reported within 6 hours, and this runs on a different clock from the DPDP breach rules. Both can be triggered by one event. Our breach playbook explains how the two regimes sit together.

    Sector regulators

    The RBI, SEBI and IRDAI each have their own data rules for regulated entities, including requirements about where data is stored. Payment system data, for example, has to be stored in India. If you are a lender, payment company or insurer, the regulator’s rule often decides the architecture before DPDP does. See our fintech lawyer in India page.

    Transfers out of India

    The Act allows transfers abroad except to countries the government restricts, so there is no blanket localisation rule. In practice, sectoral rules, contractual promises to customers and any future list of restricted countries mean the answer is rarely “anywhere”. We document your transfer position and keep it current.

    Global products

    If your product also serves the EU, the UK or California, the same flows may have to satisfy several laws at once. Our global data protection and privacy services cover those regimes, and we coordinate so you do not end up with three inconsistent sets of documents. For cookies, see cookie compliance across jurisdictions and our cookie policy drafting service.

    Who hires a data protection lawyer in India

    The questions differ by business. These are the ones we are asked most.

    Controller or processor? Enterprise customers ask for a DPA and a security annex before they sign. Who is bound by what in your sub-processor chain?

    Personal data in training sets and prompts, user consent for model improvement, and what you can promise customers about retention.

    KYC data, credit data, data shared with partners, and the overlap between RBI directions and DPDP.

    Parental consent, age checks and the ban on tracking and targeted advertising directed at children.

    Customer and seller data, logistics partners, marketing consent, and retention of order data.

    Investors increasingly ask for a privacy questionnaire. A clear, accurate answer is easier to give if the work was done earlier.

    Foreign companies with Indian users

    If you offer goods or services to people in India, the Act can reach you from abroad. We help you decide what to build, document and appoint locally.

    A monthly legal retainer for continuing privacy questions, vendor reviews and new product launches.

    Lawyer, tool or template: which do you need?

    We would rather tell you honestly when you do not need us yet.

    A tool or template is usually enough when

    You run a small site or app, collect basic contact data, use a handful of standard vendors and have no regulated or children’s data. Start with the DPDP website scanner, the compliance checker and a properly written privacy policy.

    You want a lawyer when

    You process sensitive or high-volume data, serve children, rely on many vendors, operate in a regulated sector, sell to enterprise customers who send questionnaires, expect to be designated a Significant Data Fiduciary, have had an incident, or have received a complaint or a notice. Also when a deal depends on your answers: an investor, an acquirer or a bank.

    You want a formal written opinion when

    A counterparty or board needs the legal position on a specific data question in writing, for example whether a particular transfer or processing activity is permitted. That is a legal opinion in India.

    Advocates who also draft your documents and contracts.

    My Legal Pal’s data protection work is led by Prakhar Rai, who has more than ten years of experience advising startups and companies on corporate, technology, intellectual property and regulatory matters, including data protection in India and across borders. The same team drafts the privacy policies, data processing agreements and customer contracts that carry your obligations, so the advice and the paperwork match.

    Enrolled advocates with right of audience

    Our advocates can appear in Board proceedings and before the Appellate Tribunal on your behalf. A privacy consultant or software vendor cannot.

    Advice tied to your systems

    We start from what your product and vendors actually do, not from a generic checklist, and we ask for flow diagrams and screens, not only policies.

    One team across policy, contracts and disputes

    The lawyer who sets up your compliance programme is positioned to defend it, so you do not start from zero when something goes wrong.

    How an engagement works

    We keep it simple. First, a short call to understand the business and the urgency. Then a written scope and quote before any work starts. For a compliance programme, the work usually begins with a data and systems mapping session, followed by a risk-ranked findings list and a roadmap. For a breach, a complaint or a deal deadline, we start with the urgent step and scope the rest afterwards.

    To make the first call useful, bring a list of the systems that hold personal data, your current privacy documents, your main vendor contracts, and any notice, complaint or questionnaire you have received. Please do not send us customer personal data.

    This page is general information and is not legal advice. An advocate-client relationship starts only when we confirm an engagement in writing.

    DPDP and data protection guides, tools and services

    The work referred to above, in more depth.

    The Act, the Rules, the timeline and penalties, explained.

    GDPR, CCPA and other regimes alongside DPDP.

    What valid consent looks like and how Consent Managers fit in.

    Why consent drives the design of modern privacy law.

    Who needs an impact assessment and what it must contain.

    The first 72 hours, across regimes.

    DPDPA, GDPR and CCPA privacy policies drafted by lawyers.

    A quick self-assessment of where you stand.

    An automated scan of your live website.

    A DPA you can start from.

    A written opinion on Indian law, including data questions.

    How another jurisdiction compares to GDPR and CCPA.

    Hiring a data protection lawyer in India: questions we get

    Do I need a data protection lawyer, or can I use a tool and a template?
    For a small site with basic data and standard vendors, a scan, a checklist and a well-written privacy policy can be enough to start. You want a lawyer when you handle sensitive, high-volume or children’s data, depend on many vendors, work in a regulated sector, face investor or enterprise questionnaires, have had an incident, or have received a complaint or notice.
    What does a data protection lawyer actually do under the DPDP Act?
    Applies the law to your systems and contracts. In practice that means a gap assessment, review of consent flows and notices, vendor and processor contracts, advice on Significant Data Fiduciary status and impact assessments, breach readiness and response, cross-border transfer analysis, and representation before the Data Protection Board.
    Does my company need a Data Protection Officer in India?
    Only a Significant Data Fiduciary, a status the government assigns based on factors like data volume and sensitivity, must appoint a Data Protection Officer based in India. Other companies must still be able to respond to Data Principals and handle grievances, and many choose to name a responsible person anyway.
    Can a company process employee data without consent?
    The Act has a legitimate-use ground for processing for employment purposes and for protecting the employer from loss or liability. It is not unlimited. Monitoring, background checks and the sharing of HR data with vendors still need to be justified and documented, and anything outside employment needs a separate basis.
    Do I have to store personal data in India?
    The DPDP Act has no general localisation rule. It allows transfers abroad except to countries the government restricts. But sectoral rules can require local storage, for example for payment system data under RBI directions, and your contracts and customer promises may add limits.
    What should we do if we receive a notice from the Data Protection Board?
    Do not reply informally. Note the deadline, preserve the relevant records, and speak to an advocate the same day. The Board decides on the written record, and a voluntary undertaking, if appropriate, is better prepared before a reply is filed.
    Where do I appeal against a Data Protection Board order?
    To the Telecom Disputes Settlement and Appellate Tribunal. Appeals have their own time limits, so take advice as soon as an order is received.
    Is a data protection lawyer different from a DPO or a privacy consultant?
    Yes. A DPO is a designated role inside or outside the organisation that monitors compliance. A consultant helps with process and tools. A data protection lawyer gives legal advice that is protected by the advocate-client relationship, drafts and negotiates the contracts, and can represent you in proceedings.
    Can you work with us if we are outside India?
    Yes. Most of our work is online. If you serve users in India, the Act can apply to you from abroad, and we advise foreign companies on what to build, document and appoint in India.
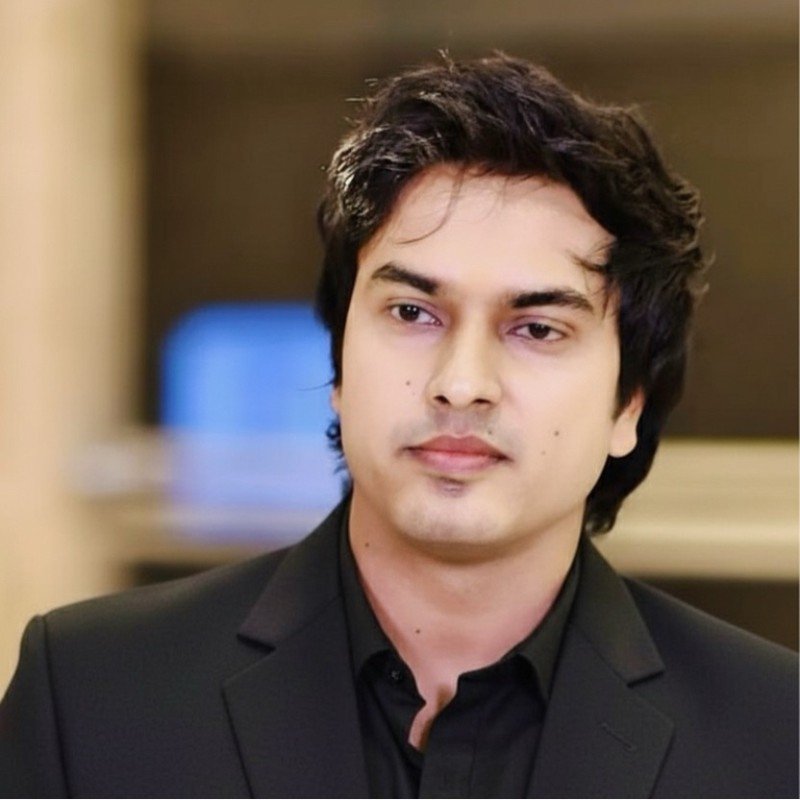
    Prakhar Rai

    Prakhar Rai | Advocate and Founder

    Written and reviewed by the advocate who leads this practice.

    This page is written and reviewed by Prakhar Rai, an advocate enrolled with the Bar Council of India, an alumnus of the National Law School of India University (NLSIU), Bangalore, with a Master of Business Laws, and the founder of My Legal Pal. Prakhar has more than ten years of experience advising startups, companies and individuals on corporate, intellectual property, regulatory and commercial matters, including data protection and technology law in India and across borders.

    Reviewed for legal accuracy by Prakhar Rai, Advocate (Bar Council of India). Last updated: October 2026.

    Talk to a data protection lawyer before the deadline, or before the notice.

    Tell us what data you handle and what is worrying you. An advocate from our team will call you back with a clear plan. No obligation.

    Call +91 8004800100